Writeup
Room404 - TryHackMe
CTF dari TryHackMe dengan difficulty easy yang berfokus pada kerentanan git exposed di web yang biasanya sering terlewat untuk developer amatir, menunjukkan bahaya nya commit history yang bisa di intip...
- Platform
- TryHackMe
- Category
- web
- Difficulty
- easy
2 min read
He booked the quiet room. It's not on the floor plan, not in the brochure, not on any door. But port 8080 is wide open, and the rooms it never lists are the ones worth finding.
bash
$ nmap -sC -sV -oA nmap/initial 10.48.139.155 --reason
Starting Nmap 7.99 ( https://nmap.org ) at 2026-10-19 22:55 +0700
Nmap scan report for 10.48.139.155
Host is up, received echo-reply ttl 62 (0.095s latency).
Not shown: 998 closed tcp ports (reset)
PORT     STATE SERVICE REASON         VERSION
22/tcp   open  ssh     syn-ack ttl 62 OpenSSH 9.6p1 Ubuntu 3ubuntu13.16 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 66:27:5f:87:d1:8b:5b:78:03:d3:99:19:f5:b4:0d:c3 (ECDSA)
|_  256 5d:2d:22:8e:c0:4f:5b:08:50:e4:a3:bf:6b:85:45:e6 (ED25519)
8080/tcp open  http    syn-ack ttl 62 Werkzeug httpd 3.0.1 (Python 3.12.3)
|_http-title: Byte Lotus — Stay Noticed
| http-git:
|   10.48.139.155:8080/.git/
|     Git repository found!
|     Repository description: Unnamed repository; edit this file 'description' to name the...
|_    Last commit message: initial Byte Lotus guest platform
|_http-server-header: Werkzeug/3.0.1 Python/3.12.3
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 15.45 seconds
hasil dari nmap menunjukkan 2 port yang open disitu ke leak bahwa ada git repo open sip, namun coba cek dulu flow web nya
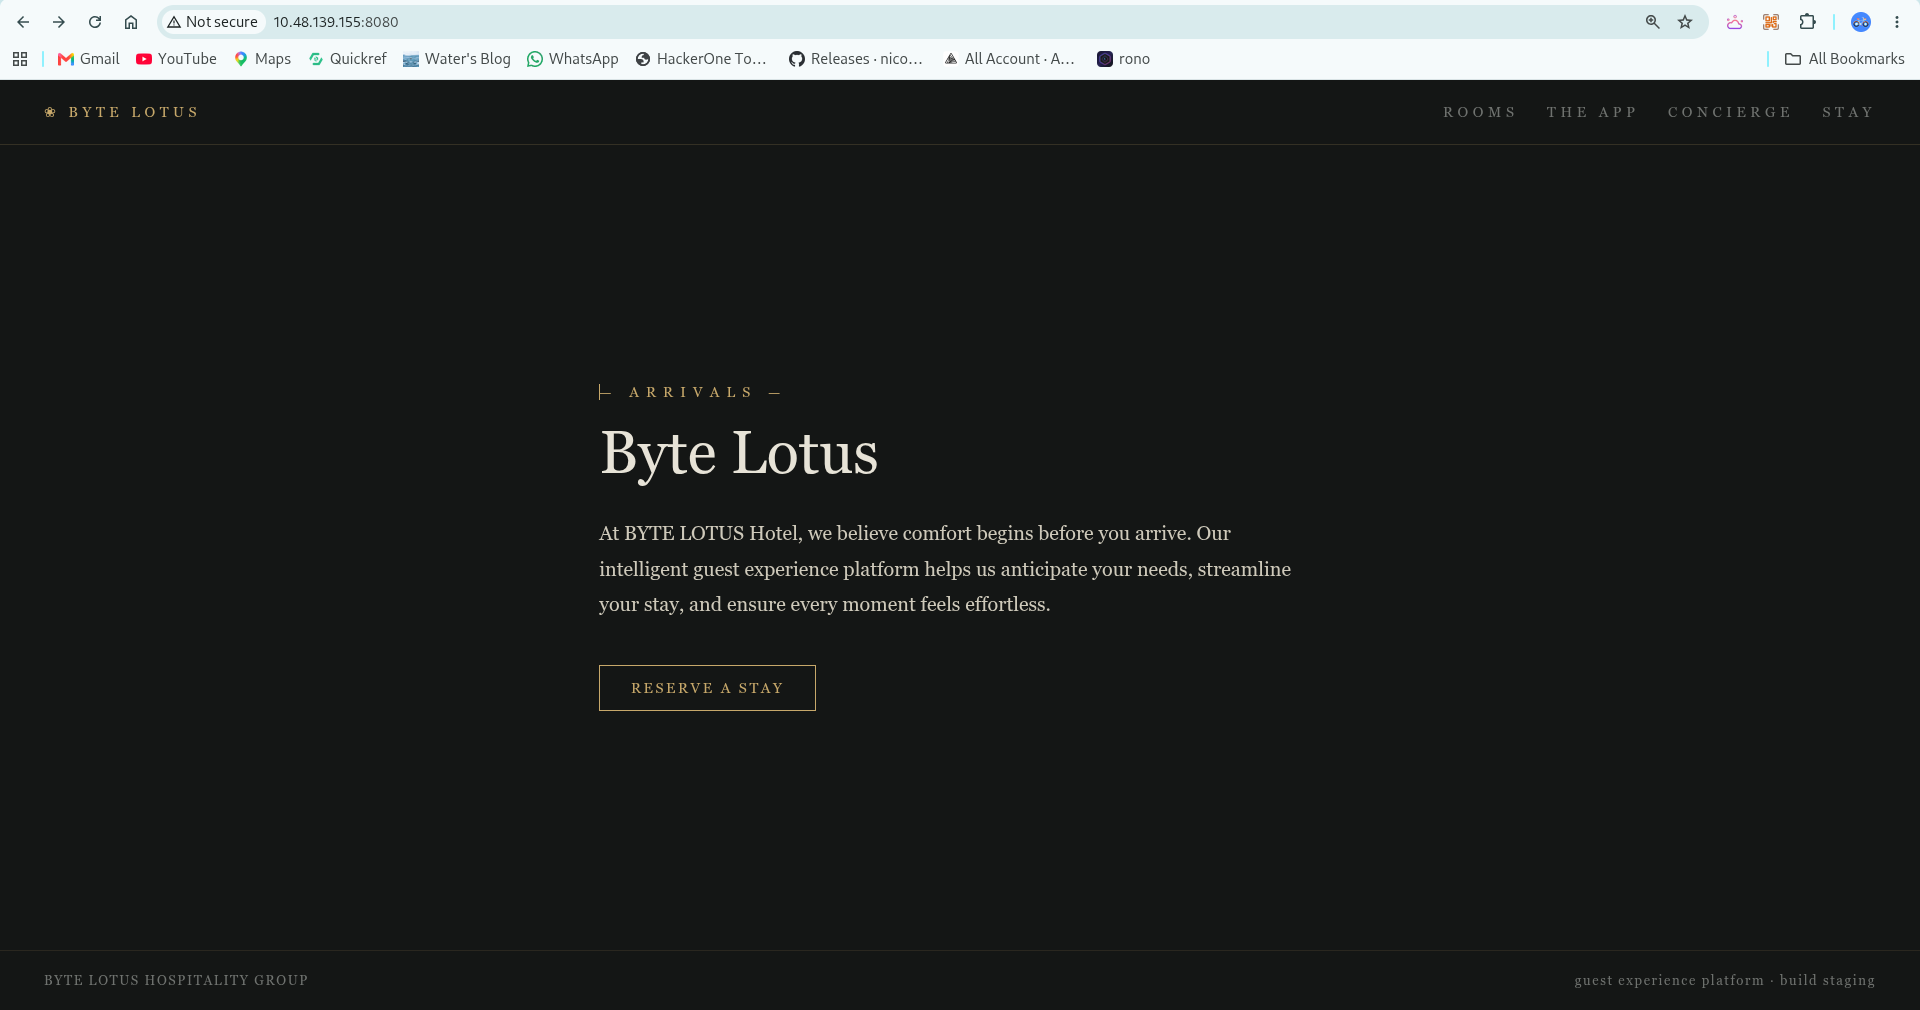
terdapat landing page normal yang ketika di klik reserver a stay akan di bawa di /booking namun page tersebut tidak ditemmukanalias return http 404
oke coba kembali ke landing page dan akses .git yang leak tersebut
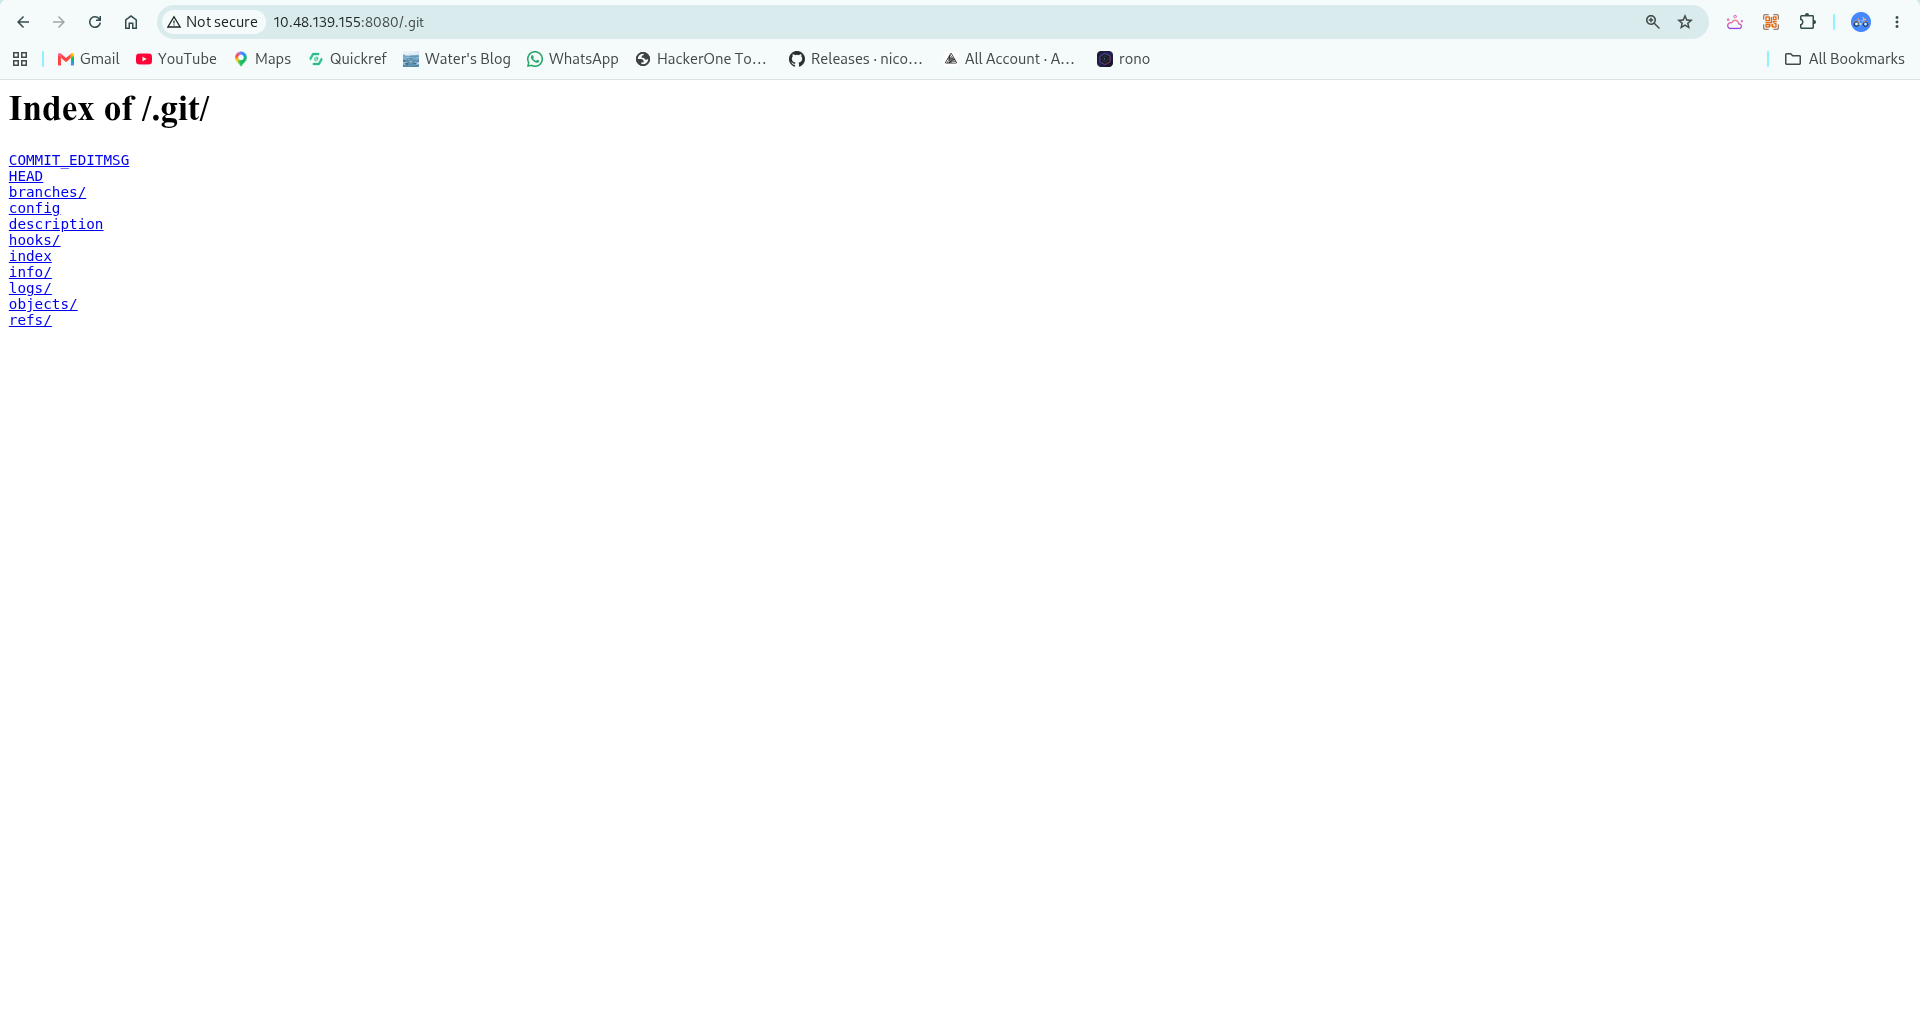
ternyata ril bocor loh ya, next dump menggunakan git-dumper